Configuring SAML Authentication for Microsoft Entra ID
For Veeam Backup & Replication to be able to use Microsoft Entra ID as an identity provider, you must perform the steps described in this section.
Step 1. Obtain Service Provider Settings
To obtain the service provider authentication settings, do the following:
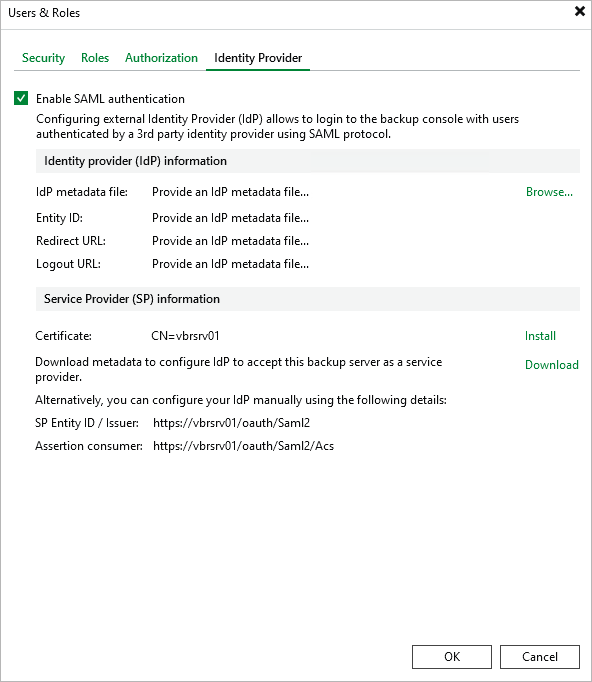
- From the main menu, select Users & Roles.
- In the Users & Roles window, select the Identity Provider tab.
- Select the Enable SAML authentication check box.
- In the Service Provider (SP) information section, do the following:
- Select a certificate that Microsoft Entra ID will use to validate requests from the backup server. By default, Veeam Backup & Replication uses the current backup server certificate.
To use a different certificate, click Install and select an existing certificate from the certificate store or import a certificate from a file. For more information, see Backup Server Certificate.
- Click Download to get the service provider settings for Microsoft Entra ID. Veeam Backup & Replication exports the XML metadata file together with a separate file that contains the public part of the SP certificate. Alternatively, you can copy the service provider settings manually.
Step 2. Set up Single Sign-On with SAML for Microsoft Entra ID Application
To set up single sign-on (SSO) with SAML in Microsoft Entra ID, do the following:
- Log in to the Microsoft Entra admin center.
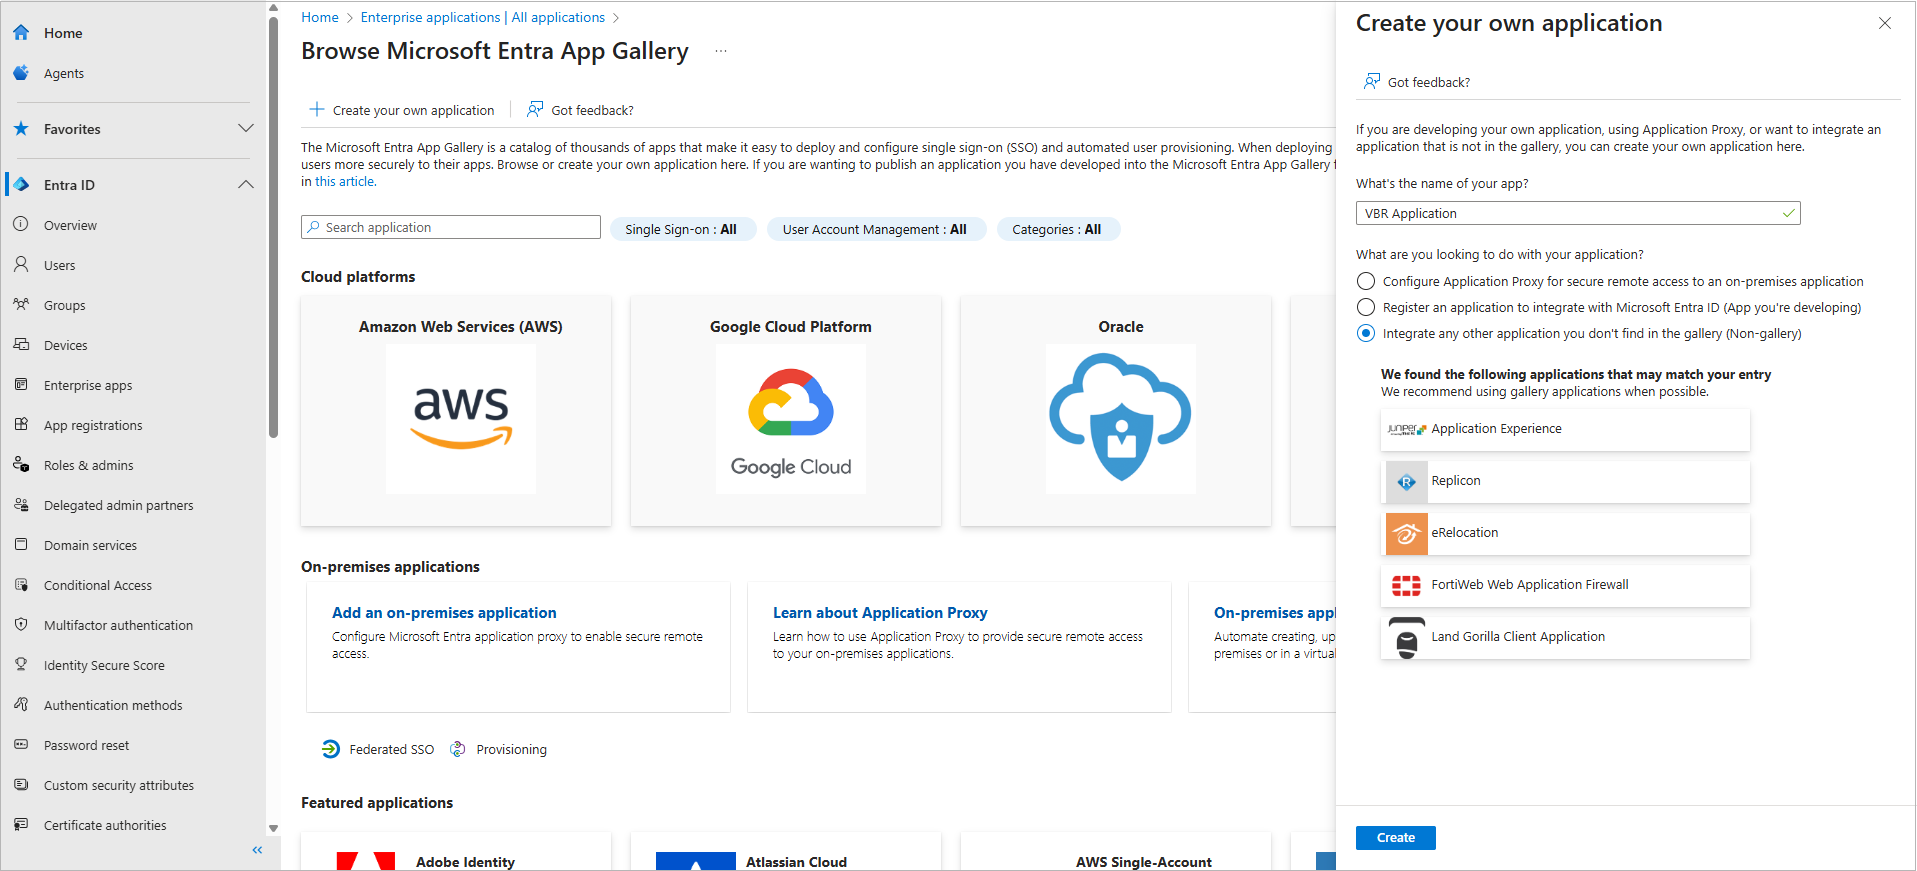
- Navigate to Enterprise apps and click New application > Create your own application.
- In the Create your own application window, specify a name for your Microsoft Entra ID application and select the Integrate any other application you don't find in the gallery (Non-gallery) option.
- Click Create.
- In the newly created application, navigate to Single sign-on and click SAML.
Step 3. Forward Service Provider Settings to Microsoft Entra ID
To forward the service provider authentication settings to Microsoft Entra ID, do the following:
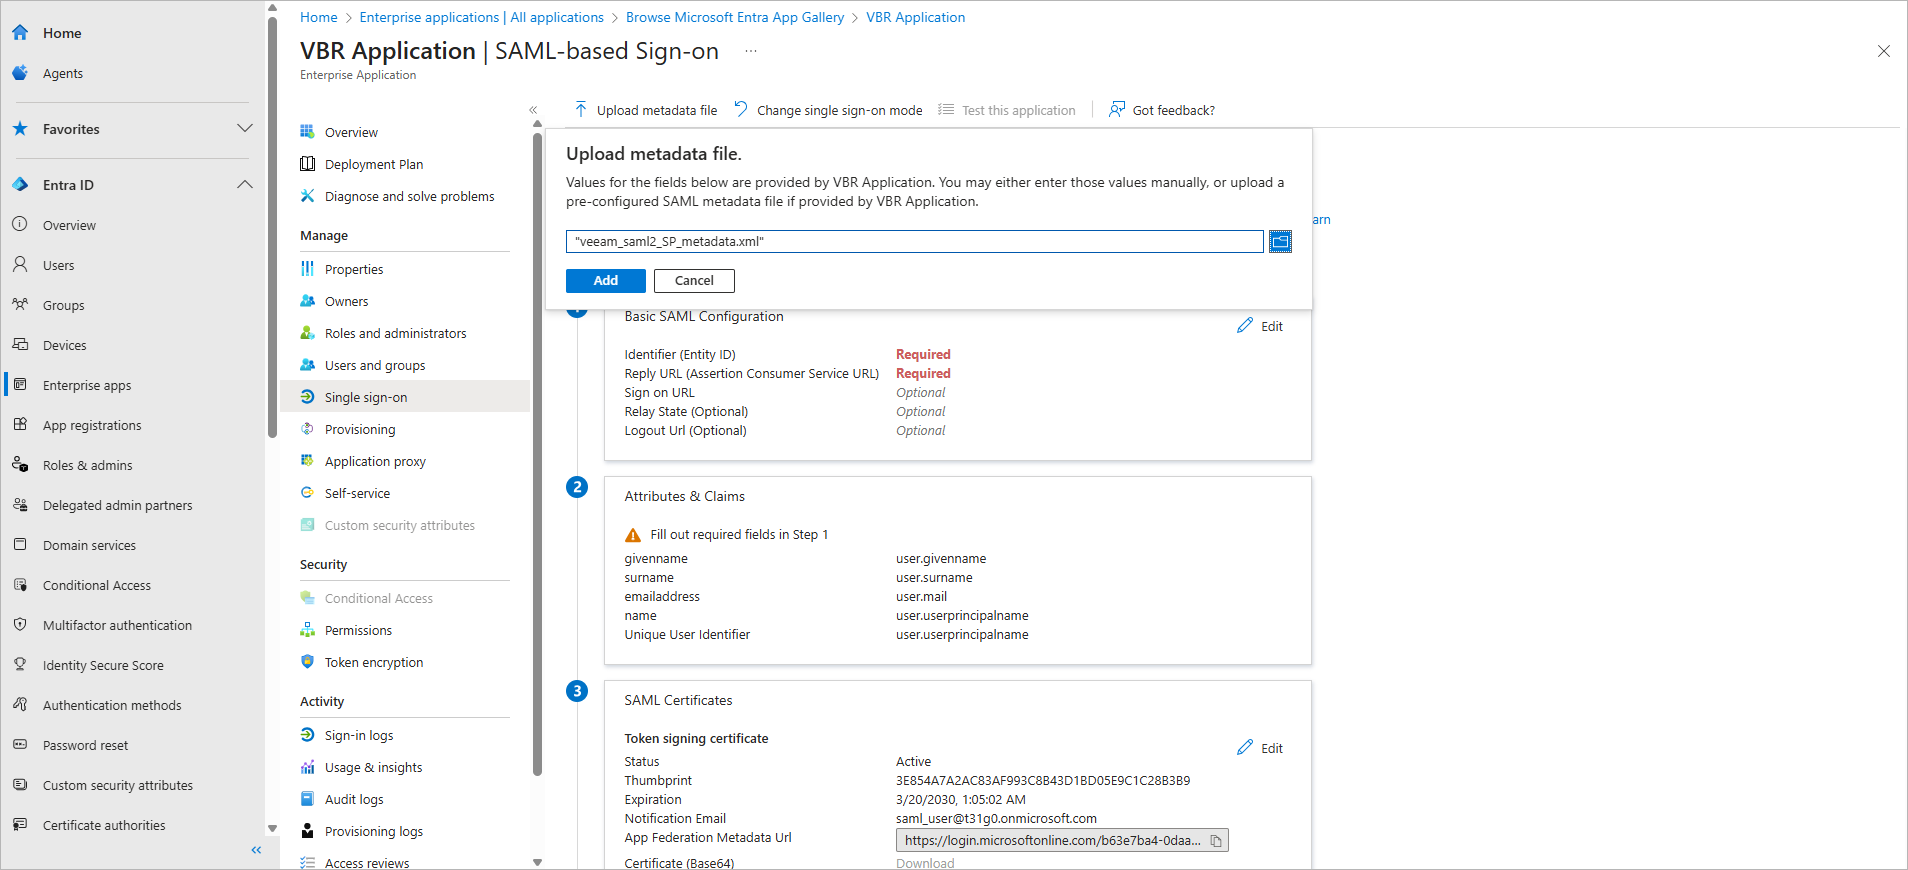
- In the Single sign-on window of your Microsoft Entra ID application, click Upload metadata file.
- In the Upload metadata file window, click the folder icon to locate the metadata file with the service provider settings you downloaded.
- Click Add.
- In the Basic SAML Configuration window, click Save.
Step 4. Create Claim for Microsoft Entra ID Application
To authenticate an SSO user, Microsoft Entra ID sends a SAML authentication response to Veeam Backup & Replication. The SAML response contains an attribute that will be used by Veeam Backup & Replication to identify the user. To send the attributes required for user-based or group-based authentication, you must create the appropriate claim in Microsoft Entra ID.
Creating Claim for Individual Users
To be able to authenticate SSO users in Veeam Backup & Replication, do the following:
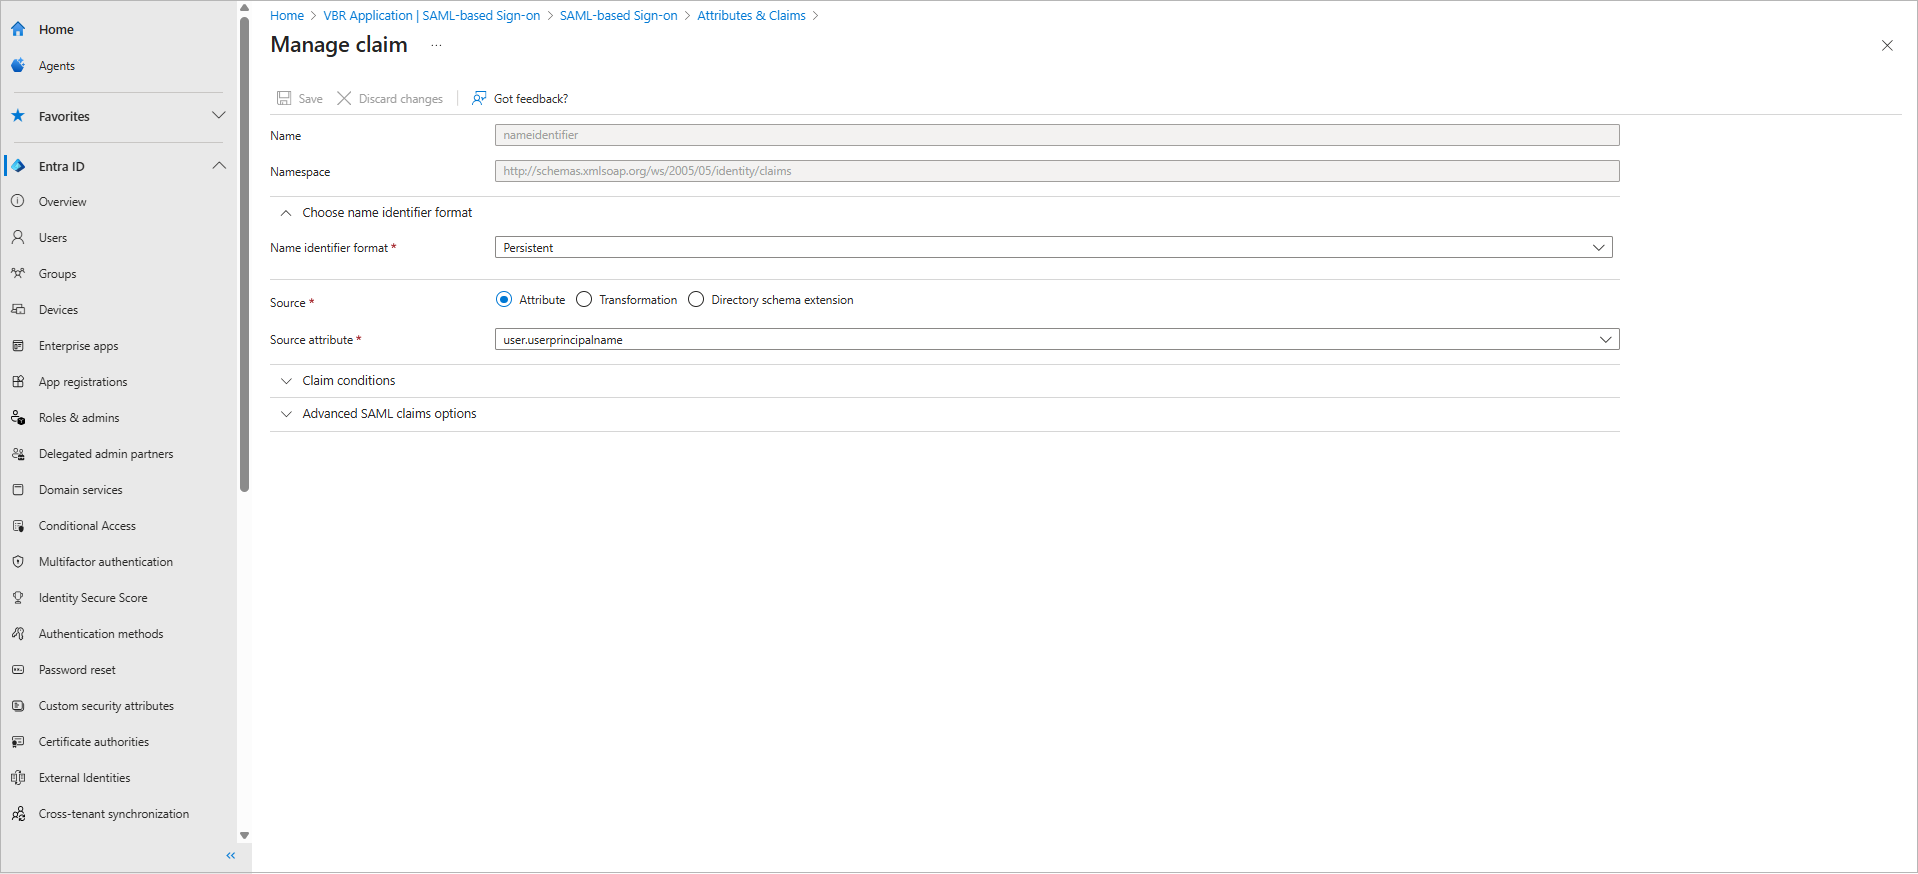
- In the Single sign-on window of your Microsoft Entra ID application, locate the Attributes & Claims section and click Edit.
- Click Unique User Identifier (Name ID).
- In the Manage claim window, set the Name Identifier Format to Persistent.
Creating Claim for Groups
To be able to use group-based SSO authentication in Veeam Backup & Replication, do the following:
- In the Single sign-on window of your Microsoft Entra ID application, locate the Attributes & Claims section and click Edit.
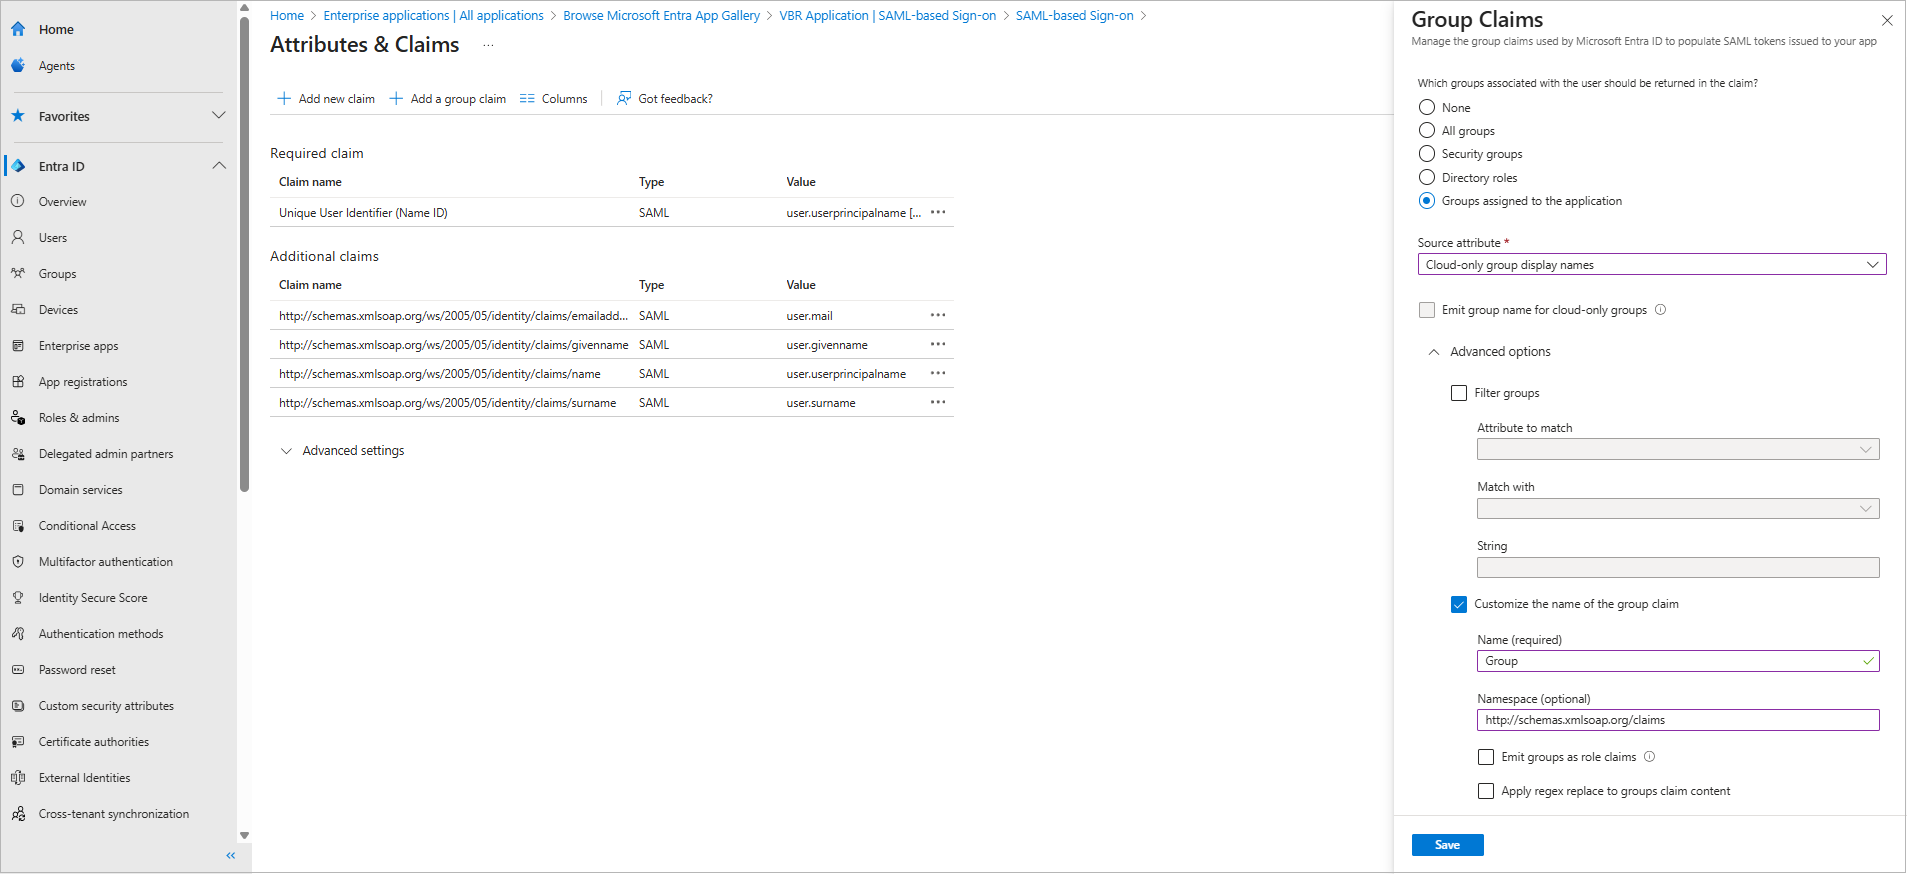
- Click Add a group claim.
- In the Group Claims window, select the Groups assigned to the application option.
- From the Source attribute drop-down list, select Cloud-only group display names.
- Expand Advanced options and do the following:
- Select the Customize the name of the group claim check box.
- In the Name field, enter Group.
- In the Namespace field, enter http://schemas.xmlsoap.org/claims.
- Click Save.
Step 5. Obtain Microsoft Entra ID Metadata
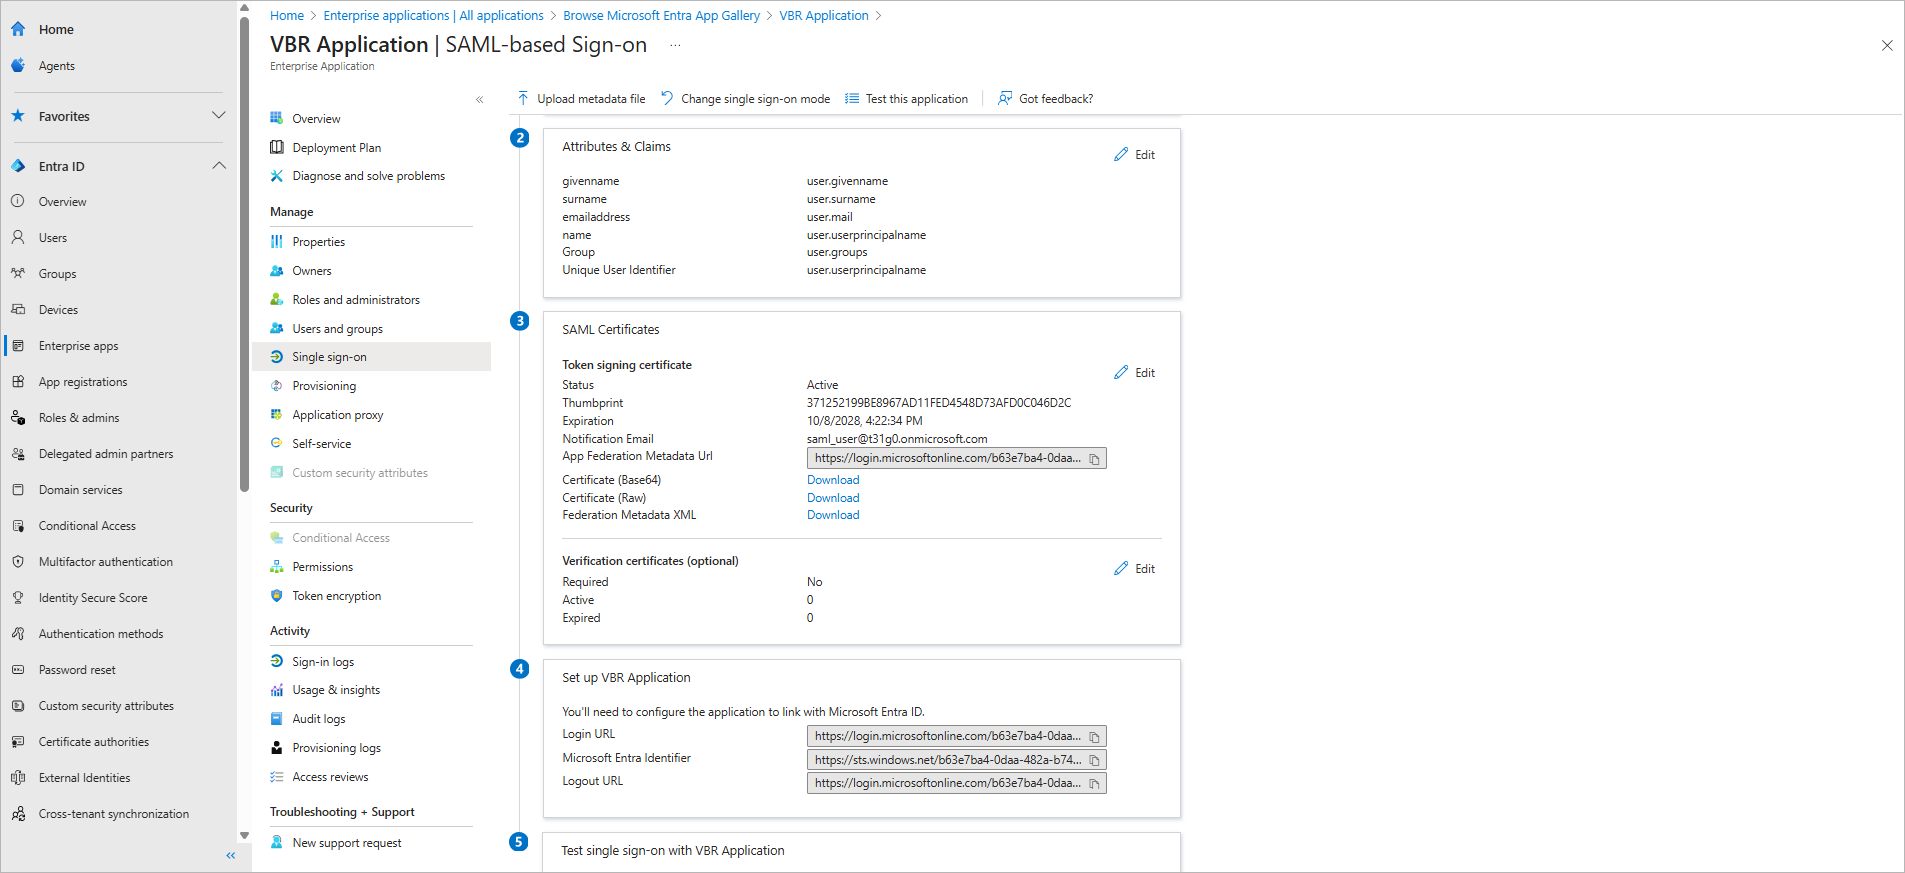
To obtain the Microsoft Entra ID identity provider settings, do the following:
- In the Single sign-on window of your Microsoft Entra ID application, locate the Federation Metadata XML field in the SAML Certificates section.
- Click Download.
Step 6. Import Microsoft Entra ID Metadata
To import the obtained Microsoft Entra ID identity provider settings to Veeam Backup & Replication, do the following:
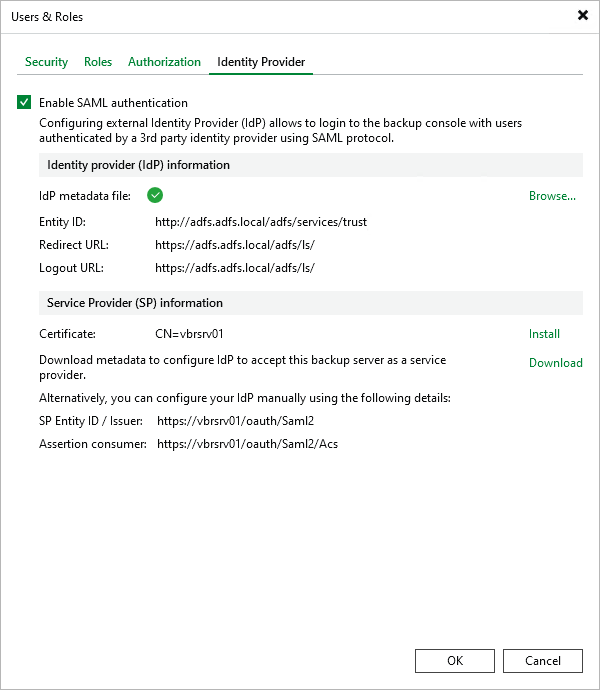
- From the main menu, select Users & Roles.
- In the Users & Roles window, select the Identity Provider tab.
- In the Identity provider configuration section:
- In the Identity Provider information section, click Browse to locate the federation metadata file with the identity provider settings.
- Click Open.
- Click OK.
Step 7. Assign SSO Users
To assign users that will be able to access Veeam Backup & Replication using SSO, do the following:
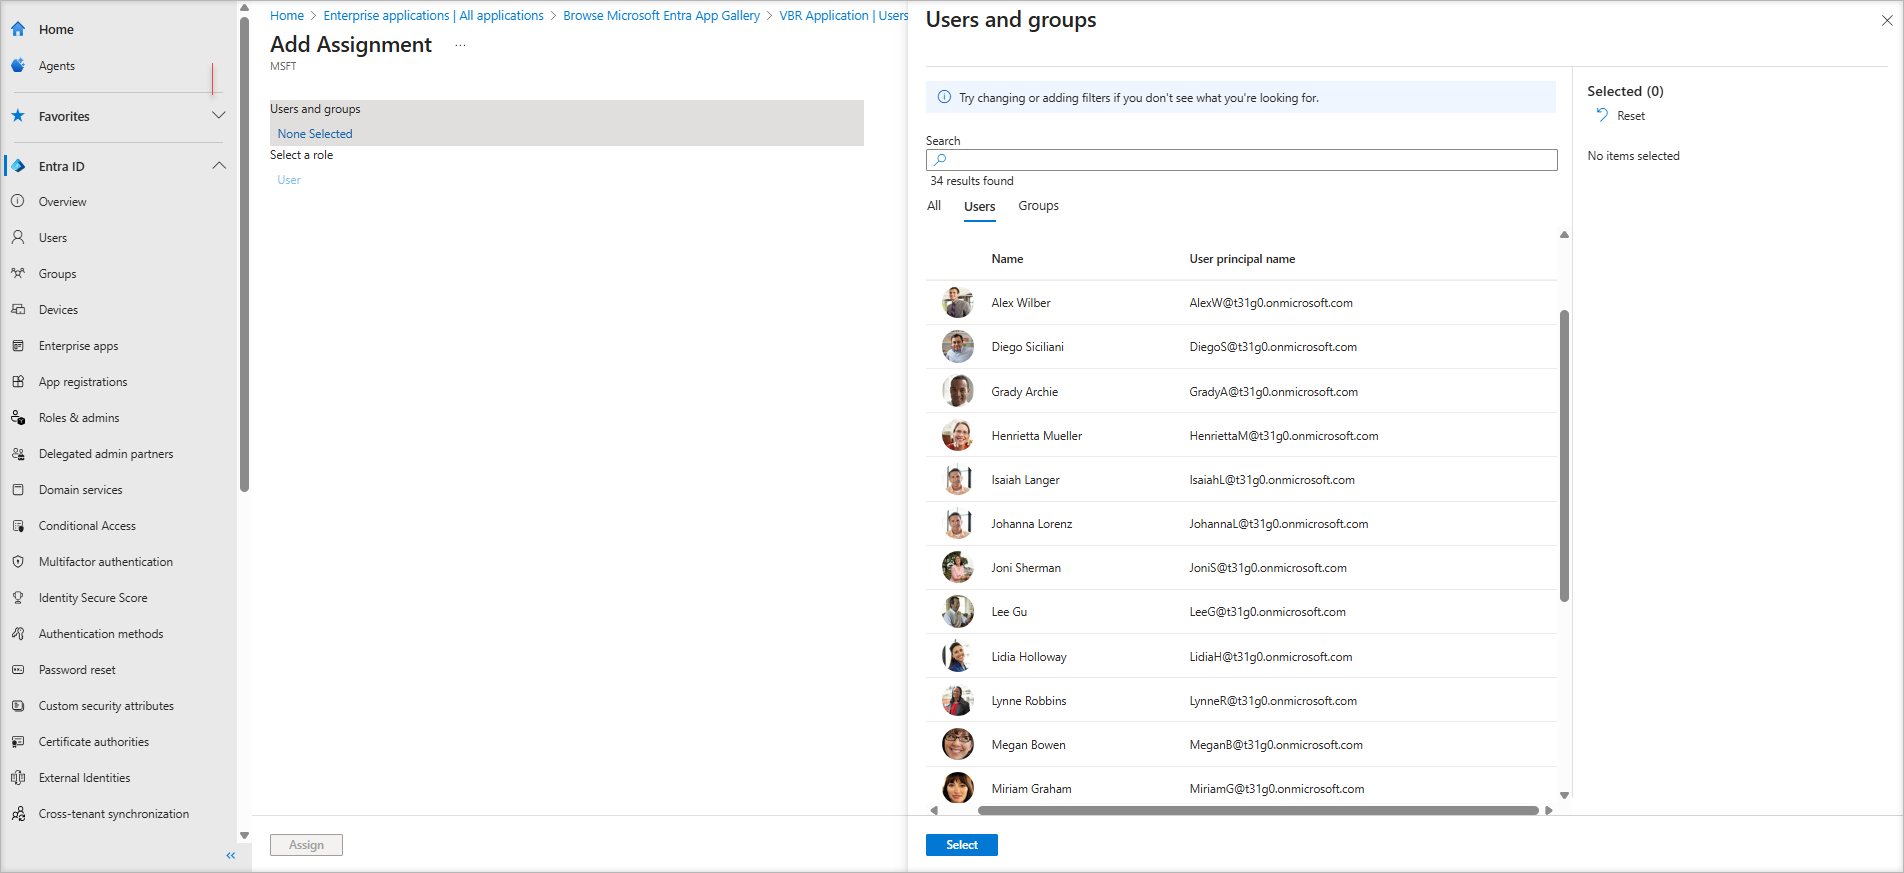
- In the Single sign-on window of your Microsoft Entra ID application, navigate to Users and groups.
- Click Add user/group.
- In the Add assignment window, click None selected and select users in the Users list.
- Click Assign.
Step 8. Add External User or Group
You can add external users or groups and assign roles to them in the Veeam Backup & Replication console or web UI.
Adding External User or Group Using Console
To add an external user or group in the Veeam Backup & Replication console, do the following:
- From the main menu, select Users & Roles.
- In the Users & Roles window, select the Security tab.
- Click Add > External user or group.
- From the Type drop-down list, select User or Group.
- In the Name field, enter the group name or user name in the UPN format, for example, john.doe@domain.com.
- From the Role drop-down list, select the role that you want to assign to this user or group.
- Click OK.
Adding External User or Group Using Web UI
To add an external user or group in the Veeam Backup & Replication web UI, do the following:
- From the top bar, select Configuration > Users & Roles.
- Click Add.
- From the Type drop-down list, select External User or External Group.
- In the Name field, enter the group name or user name in the UPN format, for example, john.doe@domain.
|
Important |
|
When specifying a group name, do not include the domain. |
- From the Role drop-down list, select the role that you want to assign to this user or group.
- Click OK.